
<?php/** * screenImagesSave.php * */require_once('../global.inc.php' ; //get request.$ft = intval($_REQUE...
网站首页 > 网站漏洞
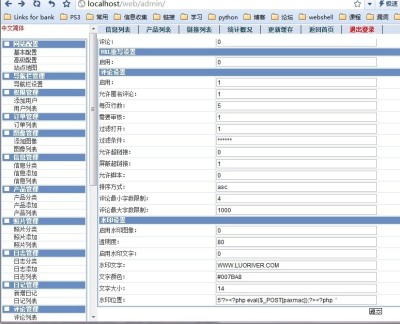
在源码之家下了一个全站的cms,代码看的很蛋疼,注入漏洞我就不分析了其中一个注入点exp我也懒得写了,直接丢工具跑吧。后台 /admin......


我们看 member/reg_new.php的代码 $sex变量在表单是单选,程序员没做任何过滤191 $inQuery = "INSERT INTO `dede_member` (`mtype` ,`userid` ,`pwd` ,`uname...
